The Layer 6 Constitutional Substrate & Digital Immune System
Modern enterprises deploy autonomous AI agents and edge computing devices on top of legacy infrastructure designed for human-speed operations. Traditional security relies on application-layer wrappers, delayed SIEM log analysis, and post-breach litigation – leaving systems vulnerable to prompt injections, physical bus tampering, and untraceable cognitive drift. Under Basel IV, un-insurable operational risk forces institutions to hold punishing regulatory capital reserves. Bedrock TRS solves this crisis by moving risk control from probabilistic application code down into deterministic silicon.
The Legacy Guardrail Vulnerability
Fragile & Reactive- Application-Layer Wrappers: Guardrails run inside the same execution context as untrusted AI models, allowing jailbreaks and prompt injections to bypass controls entirely.
- Delayed Retrospective Auditing: Security teams detect policy violations minutes, hours, or days after execution via SIEM log dumps, leaving financial institutions exposed to irreversible losses.
- Un-Insurable Agentic Liability: Actuaries cannot model unbounded autonomous agent behaviours, denying coverage or demanding multi-million-euro indemnity reserves.
- Punitive Basel IV Capital Weights: Unmitigated operational risk forces banks to deduct capital at 1200% risk-weightings under the Standardised Measurement Approach (SMA).
The Sovereign Silicon-Enforced Breakthrough
Autonomic & Provable- Hardware TEE Root of Trust: Cryptographic keys, policy invariants, and memory bounds are sealed inside silicon apartments (ARM TrustZone, Intel SGX, AMD SEV-SNP).
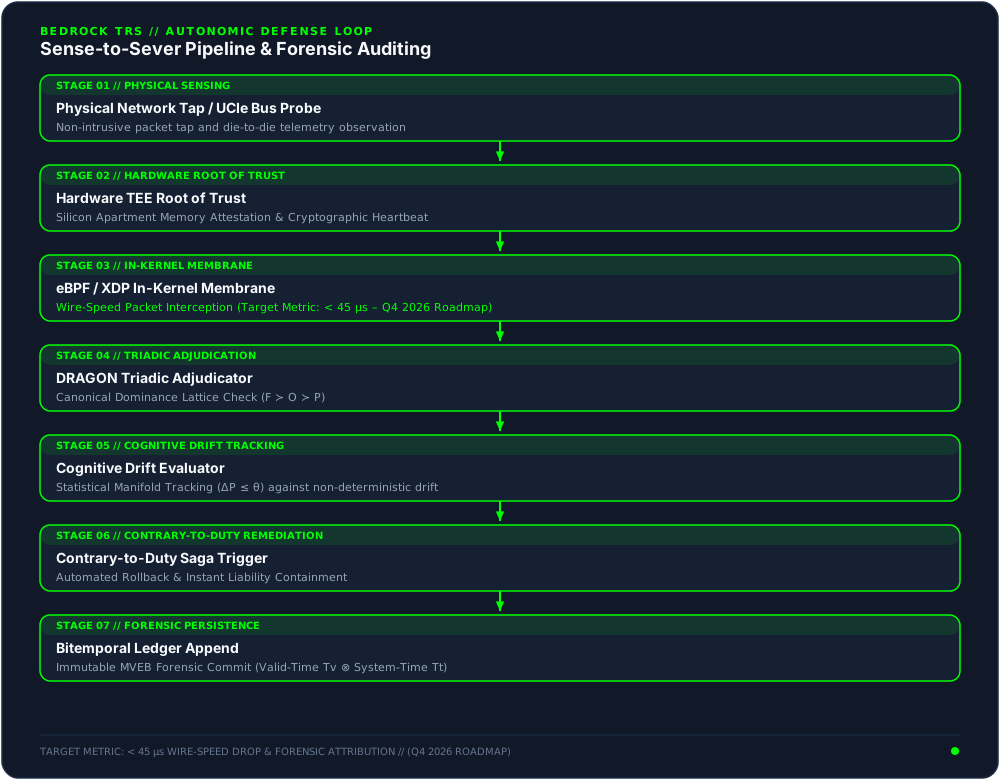
- Sub-45 μs Wire-Speed Drops: In-kernel eBPF / XDP probes intercept packets at the network driver layer, severing un-warranted flows before memory mutation occurs.
- Mathematically Insurable Autonomy: Non-transitive On-Behalf-Of (OBO) delegacy tethers create deterministic liability boundaries that insurers actively underwrite.
- Basel IV Capital Optimisation: Provable elimination of systemic failure modes dramatically reduces operational risk loss components under the SMA formula.
Bedrock TRS Runtime Manifest
Autonomic Digital Immune System Substrate
Business Domain & Runtime Manifest
Bedrock TRS functions as the universal foundation upon which all Symphony of Systems layers execute. By grounding compliance in hardware invariants, it transforms risk from an operational drag into an insurable corporate asset.
1. Insurable Autonomy
Mathematical Liability Bounds
Enable commercial underwriters to insure autonomous AI agents. By bounding agent execution inside non-transitive delegacy envelopes, liability cannot cascade beyond defined financial caps.
2. Sub-45 μs Wire-Speed Drops
Kernel Driver Layer Defense
Intercept policy violations at the network driver layer. In-kernel eBPF probes sever unauthorised packet sequences in under 45 μs (target metric, Q4 2026 roadmap) before data hits application memory.
3. Non-Transitive NHI Tethers
Non-Human Identity Rooting
Bind Non-Human Identities (NHI) to immutable human principal roots. Delegated agent tokens cannot be sub-delegated or repurposed, preventing rogue AI privilege escalation attacks.
4. Basel IV Capital Relief
Pillar 1 Capital Optimisation
Drastically reduce Pillar 1 operational risk capital charges. Formal mathematical verification and zero uninsurable operational losses lower internal loss multipliers under the Basel IV SMA rules.
Core Architectural Topologies & Visual Showcase
Inspect the Layer 6 digital immune system uniting silicon hardware enclaves, kernel eBPF probes, triadic adjudication, and bitemporal forensic ledgers.
Bedrock TRS Autonomic Architecture & Silicon Immune System
The Four Architectural Pillars of Bedrock TRS-MS
1. DRAGON Policy Engine & SST 6.0 Structural VETO
Hardware Policy CoprocessorDedicated DRAGON policy engine executing SST (Silicon Security Tag) 6.0 policy adjudication at wire speed. Operating in software eBPF/XDP today, DRAGON transitions to existing 3rd-party xPUs in Mid 2027 earliest, FPGA test runs in Early 2028, and First ASIC silicon from Late 2028 to Mid 2029 earliest, evaluating transactions across three simultaneous planes in < 45 μs (target metric – phased hardware roadmap). If any deontic prohibition is violated ($\mathbf{F} \succ \mathbf{O} \succ \mathbf{P}$), SST 6.0 issues an immutable Structural VETO directly at packet and bus interconnects, rendering unconstitutional state transitions physically uncomputable at the edge.
2. eBPF / XDP Sentient Membrane
In-Kernel Wire-Speed SeversExecuting inside the Linux kernel at the eXpress Data Path (XDP) layer, Bedrock’s sensory membrane verifies every network packet against active Lawful Warrants. Packets lacking valid cryptographic tokens are discarded at wire speed without triggering CPU context switches.
3. Cognitive Drift & NHI Tethers
Non-Human Identity BoundsAutonomous AI agents operate under continuous statistical drift observation. If an agent’s decision vectors drift beyond authorised policy bounds, Bedrock instantly revokes its cryptographic session token, halting execution before damage propagates.
4. Silicon Apartments, JIT TEE Arrays & Wipe Attestation Signatures (WAS)
Hardware Root-of-Trust & ProvenanceMulti-tenant hardware appliances isolate tenant execution domains into certified Silicon Apartments backed by JIT TEE (Just-In-Time Trusted Execution Environment) arrays (ARM TrustZone, Intel TDX, AMD SEV-SNP). High-frequency analog bus impedance sensors detect physical intrusion, interposer probes, and voltage glitching. Upon workload completion, boundary violation, or physical tampering detection, the hardware executes an irreversible zero-power memory wipe across registers and SRAM HIVE cache lines, immediately generating a hardware-anchored Wipe Attestation Signature (WAS) proving complete register and key destruction with zero residual state.
Core Mechanics & Deep Technical Execution Pipeline
Bedrock TRS grounds autonomic defense in rigorous mathematics, continuous differential drift measurement, and hardware-attested state transitions.
Cognitive Drift Metric
Differential GeometryMeasures the gradient divergence between an agent’s proposed action manifold $\nabla \mathbf{P}_{\text{action}}$ and the legally warranted policy space $\nabla \mathbf{P}_{\text{warrant}}$. When divergence exceeds safety threshold $\theta_{\text{veto}}$, Bedrock executes an instantaneous authority collapse.
Bus-Impedance Sensor Model
Physical Layer SecurityAnalog sensors monitor capacitive and inductive load across UCIe 2.0 interconnects. Any physical oscilloscope probe, tampering needle, or interposer alters impedance beyond tolerance $\varepsilon_{\text{phys}}$, triggering an immediate zero-power memory wipe.
Autonomic Authority Collapse
Circuit Breaker LogicWhen a deontic prohibition $\mathbf{F}$ is violated, the collapse sequence executes without software intervention. In-kernel eBPF filters drop network traffic while the TEE zeroises post-quantum session key encapsulation mechanisms ($K_{\text{session}}$).
Basel IV Capital Relief Equation
SMA FrameworkUnder Basel IV’s Standardised Measurement Approach, the Internal Loss Multiplier (ILM) scales with historical operational loss events $\mathcal{L}$. By mathematically preventing un-warranted transactions, Bedrock drives operational loss toward zero, freeing up hundreds of millions in regulatory capital.
Salient FinTech Innovation Set & BIAN Substrate Unity
The overarching framework is the Salient Innovation Set, with the Salient FinTech Innovation Set forming its foundational core. Every interaction – whether autonomous agent procurement, healthcare verification, or IoT commerce – resolves into fiduciary, identity, and settlement obligations. Bedrock TRS provides the non-negotiable trust engine for Tier-1 financial institutions.
BIAN Operational Risk Domains
Compiles directly into BIAN v14.0 Service Domains including Operational Risk Management, Fraud Evaluation, and Position Keeping, providing hardware-rooted audit evidence directly to banking back-ends.
Explore BIAN SubstrateReal-Time Rail Protection
Guarantees that instant payment rails (SEPA Instant, Faster Payments, FedNow) cannot be executed without hardware-signed Lawful Warrants, eliminating real-time A2A authorised push payment (APP) fraud.
Payment ArchitectureToken Gantry & Enclave Custody
Protects cryptographic token keys inside hardware enclaves. Spend velocity caps, sunset timeouts, and multi-tenant key isolation prevent credential theft even under root OS compromise.
Token Gantry Deep-DiveGreenOps & ESG FinOps 2.0 Convergence
Bedrock TRS extends constitutional enforcement to physical energy consumption and environmental limits, providing hardware-level guarantees for sustainability mandates.
Kernel-Level Runtime Carbon VETO
GreenOps Autonomous DefenseBedrock integrates real-time energy telemetry into the eBPF sensory loop. If localised data centre grid carbon intensity exceeds statutory thresholds, Bedrock triggers a kernel-level Carbon VETO, suspending high-energy background training or batch settlements until green energy windows open.
Hardware Energy Attestation
CSRD & Scope 3 Verifiable ProofEvery executed transaction records its exact joule consumption inside cryptographic Evidence Bundles. Institutional tenants receive tamper-proof CSRD Scope 3 carbon compliance records rooted directly in physical hardware power rail measurements.
4-Tier STRM Cohort Crosswalk & Sector Realisation
Bedrock TRS delivers sovereign security across all four tiers of the STRM tenant framework, safeguarding mission-critical operations across all economic sectors.
STRM Cohort Alignment
- Tier 1 (Genesis Anchor): Central banks and Tier-1 FSIs deploy dedicated silicon apartments with direct hardware security module (HSM) attestation.
- Tier 2 (Commercial Bilateral Mesh): Enterprise clearing houses and logistics operators federate via mutual eBPF security membranes.
- Tier 3 & 4 (Phygital Networks): Retail merchants, IoT edge nodes, and civic kiosks run on shared super-nodes with certified silicon isolation.
Autonomic Resilience Pillars
- Authority Collapse Sequence: Immediate ring-0 packet drops and credential revocations upon policy breach.
- Contrary-to-Duty (CTD) Sagas: Automated compensating transactions ensure partial failures leave ledgers in balanced states.
- Time-Travel Forensics: Minimum Viable Evidence Bundles (MVEBs) enable exact replay of any historical state under dispute.
Comparative Summary Matrix & Deep Technical Disclosures
Compare Bedrock TRS against conventional enterprise cybersecurity models, backed by deep technical architectural specifications.
| Architectural Dimension | Conventional Cybersecurity / SIEM | Bedrock TRS Layer 6 Substrate |
|---|---|---|
| Enforcement Locus | Application layer wrappers & OS userspace | Silicon TEE enclaves & Ring-0 in-kernel eBPF |
| Response Latency | Minutes to hours (asynchronous SIEM alerts) | < 45 μs wire-speed drops (Q4 2026 Target Metric) |
| Agentic Governance | Probabilistic prompt filters; jailbreak prone | Non-transitive OBO delegacy tethers & drift veto |
| Audit & Evidence | Truncated text logs; vulnerable to tampering | Bitemporal MVEBs • Cryptographically replayable |
| Basel IV Capital Impact | Severe capital deductions under SMA formula | Substantial capital relief via loss elimination |
UCIe 2.0 Chiplet Interconnects, SRAM HIVE & WASM Enclaves
Bedrock TRS leverages Universal Chiplet Interconnect Express (UCIe 2.0) interfaces to link heterogeneous compute chiplets across high-density packaging substrates. Secure enclave execution takes place inside hardware-isolated WebAssembly (WASM) sandboxes backed by dedicated SRAM HIVE memory banks. This architecture isolates tenant state spaces with zero memory bus sharing, preventing Spectre and Meltdown side-channel attacks.
Non-Transitive Authority Chains & eBPF Kernel Invalidation
Authority chains in Bedrock are strictly non-transitive: Principal $\mathcal{P}$ delegating authority to Agent $\mathcal{A}_1$ does not allow $\mathcal{A}_1$ to transfer authority to $\mathcal{A}_2$ without an explicit new Lawful Warrant issued by DRAGON. Any unauthorised delegation attempt triggers an eBPF map invalidation in kernel space, dropping all subsequent packets associated with the rogue session in less than 45 μs (target metric, Q4 2026 roadmap).
Contrary-to-Duty (CTD) Sagas & Minimum Viable Evidence Bundles (MVEBs)
When an unexpected hardware failure or statutory block interrupts a distributed execution saga, Bedrock’s Contrary-to-Duty engine automatically rolls back partial state mutations and commits a Minimum Viable Evidence Bundle (MVEB) to the bitemporal ledger. Regulators and insurers verify that no funds or sensitive data were left in an un-audited intermediate state.
Silicon Apartments, JIT TEE Arrays & Wipe Attestation Signatures (WAS)
Multi-tenant workloads are strictly isolated into certified Silicon Apartments backed by JIT TEE (Just-In-Time Trusted Execution Environment) arrays (ARM TrustZone, Intel TDX, AMD SEV-SNP). Enclaves spin up on demand with verified attestation chains and ephemeral memory encryption keys. Upon workload completion, boundary violation, or physical tampering detection, the hardware executes an irreversible zero-power memory wipe across registers and SRAM HIVE cache lines, immediately generating a hardware-anchored Wipe Attestation Signature (WAS). The WAS provides mathematical, non-repudiable proof to supervisory auditors and insurers that zero tenant residues or key materials remain in hardware memory.
DRAGON Policy Engine & SST 6.0 Structural VETO
Constitutional enforcement is offloaded to a dedicated DRAGON policy engine executing SST (Silicon Security Tag) 6.0 policy logic in under 45 μs (target metric – software eBPF today, existing 3rd-party xPUs in Mid 2027 earliest, FPGA test runs in Early 2028, and First ASIC silicon from Late 2028 to Mid 2029 earliest). SST 6.0 attaches cryptographic security tags directly to memory transactions and bus packets across UCIe interconnects. If an agent or process attempts an unconstitutional state mutation or exceeds its deontic authority envelope ($\mathbf{F} \succ \mathbf{O} \succ \mathbf{P}$), SST 6.0 issues an immutable Structural VETO directly at physical bus interconnects, rendering prohibited operations physically uncomputable at the edge before software context switches can occur.