Physical Boundary of Trust
The Paradigm Shift
The Failure of Checklist Governance
For decades, enterprise security and risk management have operated behind the curve. Traditional Information Security Management Systems (ISMS) treat compliance as an administrative, backward-looking paperwork exercise. Policies are drafted in text documents, interpreted by human operators, and manually configured into fragmented firewall rules, database access configurations, and user directories.
This disconnected chain leaves a significant gap for "Policy Drift" – the core source of data breaches, regulatory fines, and systemic failures in highly regulated sectors.
Active Enforcement via the Silicon Constitution
onePOI.online closes this gap entirely by introducing an active, runtime Trust, Risk & Security Management System (TRS-MS). Governed by a custom Constitutional OS and powered by the Salient Innovation Set framework, our platform embeds legal requirements, international banking standards, and cross-sector multi-tenant risk parameters directly into the physical infrastructure.
By moving compliance checking directly into the transport data plane and processor register loops, the platform enforces a singular operational invariant: non-compliance is rendered computationally unrepresentable. If an action at an edge kiosk or a code commit inside a development pipeline attempts to violate a core system rule, the architecture blocks the command at the hardware layer before it can allocate downstream memory or application resources.
The Silicon Invariant
If an action at an edge kiosk or a code commit inside a development pipeline attempts to violate a core system rule, the architecture blocks the command at the hardware layer before it can allocate downstream memory or application resources.

Continuous three-stage runtime cycle: Detection (telemetry, anomaly signals) → Validation (DRAGON adjudication against Policy Hash) → Assessment (Trust Decay scoring and escalation).
Vertical Assurance
The 6-Layer Architecture Grid
To eliminate blind spots, vulnerabilities, and configuration discrepancies, onePOI.online organises its technical and operational controls across six distinct layers of enterprise architecture. Every low-level physical trace is traceably bound back to a high-level corporate governance goal.
1. Contextual Layer
The Business View
Operational Scope: Mapping cross-sector multi-tenant environments, asset taxonomies, and strategic regulatory drivers.
The Blueprint: The platform abstracts complex, shifting international rules – including the operational resilience standards of DORA, the infrastructure protections of NIS2, and the algorithmic transparency of the EU AI Act – into clear corporate objectives.
The Invariant: Business data assets are packed as binary Law-Bound Data Products (LBDPs) wrapped in a secure Provenance Envelope, ensuring all data carries its own unalterable governing rules from the nanosecond of its creation.
2. Conceptual Layer
The Architect's View
Operational Scope: Converting high-level risk appetites into explicit, measurable metrics using a formal Business Attributes Profile.
The Blueprint: System integrity is continuously measured through active parameters: Attestation Fidelity (cryptographic confirmation of device hardware states), Lineage Verifiability (complete audit histories), and Non-Repudiation Certainty (biometric sealing of intent via Qualified Electronic Signatures).
The Invariant: Written legal parameters compile into machine-readable Deontic Primitives – Obligations, Permissions, and Prohibitions – governed by a strict dominance order where Prohibitions mathematically override all other states.
3. Logical Layer
The Designer's View
Operational Scope: Designing technology-agnostic functional engines, data pipelines, and interaction models.
The Blueprint: Cross-tenant state modifications are written as multi-directional Lawful Act Hyperedges (LAHEs) on a decentralised Merkle Bi-Temporal Hypergraph. Core policy evaluation is offloaded to the DRAGON Engine, which compresses complex rules into memory-optimised bitmasks.
The Invariant: By evaluating rules via register-level bitwise operators instead of slow graph-traversal loops, the system locks processing to a flat \(\mathcal{O}(1)\) Logic Traversal Invariant Strategy, eliminating performance bottlenecks.
4. Physical Layer
The Builder's View
Operational Scope: Hardware-enforced processing perimeters, network ingress logic, and cryptographic verification proof delivery.
The Blueprint: The architecture utilises the Multi-Tenant Confidential Computing Framework (MTCCF) to isolate multi-tenant execution. Workloads, cryptographic material, and data-in-use are completely sealed inside hardware-encrypted processor enclaves known as TEE Hardware-Isolated Enclaves.
The Invariant: Adjudicated interactions automatically emit a Minimum Viable Evidence Bundle (MVEB) – a zero-knowledge cryptographic proof capsule that allows external regulators to audit total systemic compliance without exposing consumer identity or PII.
5. Component Layer
The Tradesman's View
Operational Scope: Low-level code libraries, optimisation scripts, hardware element footprints, and compiler toolchains.
The Blueprint: Serialization is enforced via binary FlatBuffers schemas to erase application parsing latencies. The DRAGON Engine implements AVX-512 SIMD vector instructions to resolve multi-hop rules in under 450 nanoseconds.
The Invariant: Hardened edge hardware assets, such as Switcher+ Kiosks, run read-only operating systems with a low-level Physical Voltage Inversion Cycle (PVIC) that shreds memory keys within microseconds if physical chassis tampering or voltage manipulation is detected.
6. Service Management Layer
The Manager's View
Operational Scope: Omnidirectional lifecycle wrap-around monitoring, automated runtime self-healing, and continuous forensic validation.
The Blueprint: Rather than functioning as a reactive afterthought, this layer wraps around the entire ecosystem. The platform dual-indexes ledger entries across Valid-Time and Transaction-Time axes, driving a Recomputation-as-a-Service (RaaS) engine that lets operators deterministically replay historical execution trees with absolute cryptographic fidelity.
The Invariant: Unresolvable policy deadlocks trigger a freeze-frame isolate sequence, escalating the context bundle to the human-in-the-loop TopHAT Council to resolve structural ambiguities using biometric multi-signature validation.
BIAN Packaged Business Capabilities (PBCs)
To connect financial operational lifecycles with physical infrastructure enforcement, onePOI.online compiles the banking standards of the Banking Industry Architecture Network (BIAN) directly into hardware-isolated Packaged Business Capabilities (PBCs).
Offer & Product Lifecycles
Captured via strict Offer Control Records and binary RateCard DAGs, anchoring financial rulesets to a verified version hash inside the platform Registrar.
Party & Agreement Management
Instantiated inside the KnowledgeHUB as an un-spoofable Digital Twin of the Person, matching verifiable credentials and customer signatures directly to the active Agreement Control Record.
Fulfilment Operations
Governed by automated Actuator DAG Runbooks executing the Saga Pattern. If a distributed banking step fails, the system executes Compensating Stanzas to write a signed Reversal LAHE, restoring the cross-sector system state safely without global locks.
The Agentic DevSecOps Foundry
The platform pushes its compliance guardrails upstream into software development through an active Agentic Foundry. Within this cloud development environment, human engineers collaborate with autonomous iEngine Agents to prove code safety before compilation.
The Inspector Agent
Operates as an authority-poor edge validator, executing lightweight syntactic sweeps and regular expression tests to strip vulnerabilities before code enters the pipeline.
The Guardian Agent
Manages the development team's Continuous Authority to Operate (cATO). The agent performs automated Proofs of Non-Contradiction (PoNC) over Infrastructure-as-Code (IaC) updates. If a modification attempts to bypass a platform restriction, the Guardian halts the session by invalidating memory page pointers at the silicon layer.
The Composer Capability Set
Utilises a Neuro-Symbolic Architecture to monitor code synthesis in real time. If an LLM suggests an engineering snippet, the symbolic core cross-references the suggestion against the global Axiom MESH, flagging errors before bugs can compile.
The Technical Substrate
The underlying enforcement fabric and network topography that secures active compliance.
Constitutional Security Mesh Architecture (CSMA) & PEP/PDP Paths
The platform converts the network data plane into a real-time policy adjudicator using the Constitutional Security Mesh Architecture (CSMA). The **DRAGON Engine** acts as the centralised **Policy Decision Point (PDP)**, resolving complex deontic rules into AVX-512 vector bitmasks. High-performance **Policy Enforcement Points (PEPs)** are embedded directly at the OS kernel layer using **eBPF/XDP and Cilium SD-Network service meshes**.
All inter-node microservice communications are encrypted via **mTLS over WireGuard tunnels**, guaranteeing identity-attested transport. Real-time telemetry streams from kernel probes into **In-Memory Data Grids (IMDGs)**, feeding telemetry directly into **Axiom MESH** refinement loops to continuously adjust security posture based on runtime risk metrics.
Edge Resiliency: Island Mode
When an edge POI appliance encounters an unexpected cloud network disconnection, it drops into Island Mode. Transactions continue to execute securely by routing through a hardware-isolated SRAM Hive loaded with cached subsets of the legal state graph. Upon reconnection, the terminal utilises distributed Merkle-CRDTs to merge local ledger entries back into the central KnowledgeHUB, ensuring deterministic state synchronisation without data collision.
Deterministic Threat Internalization
onePOI.online internalises industry standard security matrices – including OWASP (AppSec), MITRE ATT&CK (Threat Lifecycles), and R3ACT (Incident Response) – directly into its adjudication pipeline, turning reactive security defence into deterministic execution physics.
-
1
OWASP Mitigation: Input validation constraints (regex limits, length parameters) are written directly into the Data Bill of Materials (DBOM), enabling the Syntactic Pass to drop injection attacks at line-rate at the network interface layer.
-
2
MITRE ATT&CK Invalidation: The Pragmatic Pass strictly boundaries network access within the paths of the pre-verified Legal-State Reachability Graph (LSRG). Because unauthorised lateral movement routes are topologically non-existent within the pre-compiled bitmask matrix, internal networks are physically insulated against adversary progression.
-
3
R3ACT Automation: If a policy violation occurs, eBPF-driven micro-segmentation severs the specific compromised connection at the kernel level instantly, quarantining the threat context without impacting adjacent tenant container interfaces.
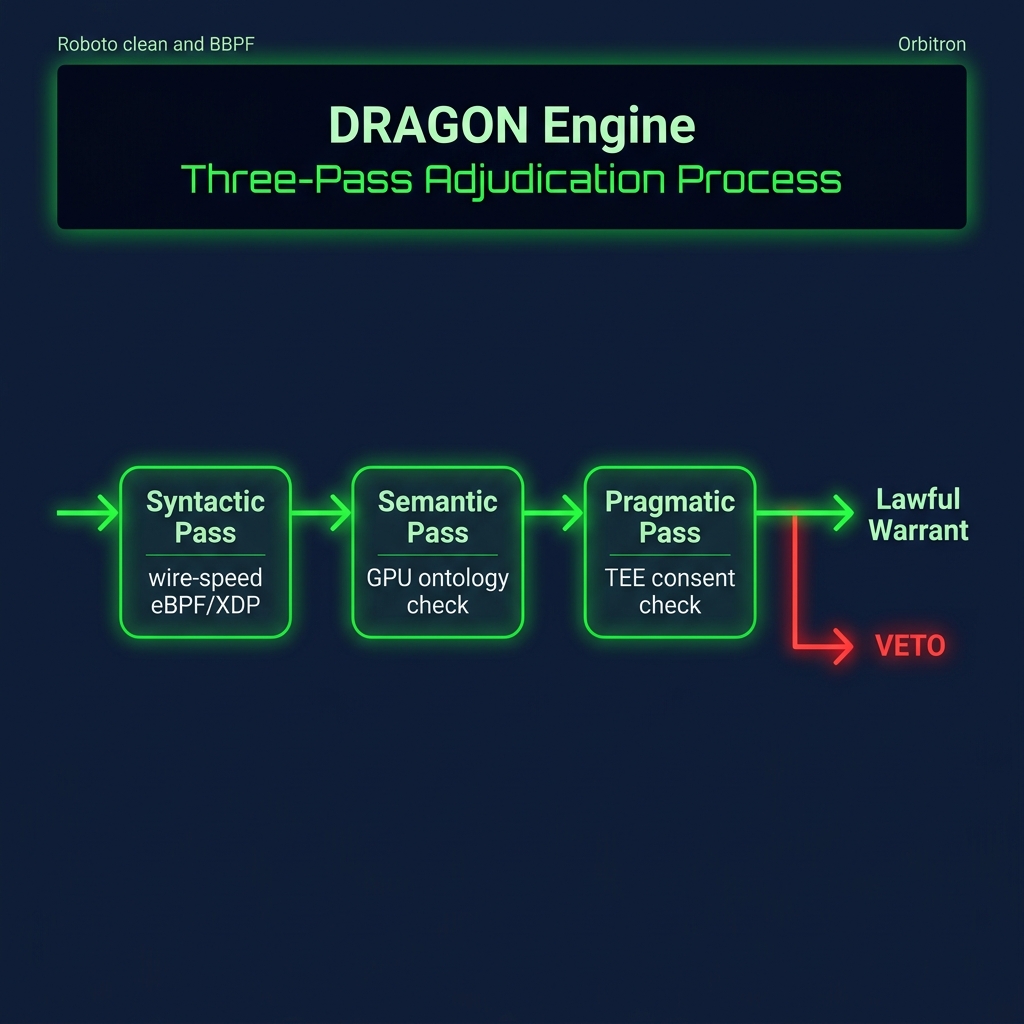
Adjudication flow: Syntactic Pass (wire-speed eBPF/XDP checking) → Semantic Pass (GPU ontology reasoning) → Pragmatic Pass (TEE jurisdiction and consent checks) leading to a Lawful Warrant or a Structural VETO.
Compliance Core Schemas
The core transaction payload block committed to the bitemporal ledger for system validation. This ledger serves as the Emotional Bedrock of Total Trust: by producing a mathematical proof of every transaction in real-time, it forms an Audit-as-a-Query ledger. If an incident or exception occurs, tenants run automated queries against the ledger to determine exactly which logic, hardware, or model state failed. This eliminates inter-tenant finger-pointing and supports Blameless Post-Mortems, since the cryptographic audit trail establishes objective truth instantly.
I. Lawful Act Hyperedge (LAHE) Wire-Trace Schema
{
  "laheId": "lahe-csma-2026-9921a",
  "policyHash": "PH-8f3a9b2c7e1d4f6a8b0c2d4e6f8a0b2c4d6e8f0a2b4c6d8e0f2a4b6c8d0e2f4a",
  "agreementDagId": "AGR-BIAN-COREPAYMENT-V4",
  "action": "ExecuteInterbankSettlement",
  "actorSVID": "spiffe://onepoi.online/pbc/agreement/settlement-engine-core-01",
  "validTime": "2026-06-15T19:35:12.123048000Z",
  "transactionTime": "2026-06-15T19:35:12.456182000Z",
  "evidenceEnvelopeRef": "mveb-77123-zkp-capsule",
  "teeAttestation": "eyJhbGciOiJSUzI1NiIsInR5cCI6IkpXVCIsImtpZCI6InRlcS1xdW90ZS1rZXkifQ...[Base64 Intel SGX / AMD SEV-SNP Enclave Quote Data]",
  "signature": "MEYCIQCc3WUhXWUp6ZThzKzVw...[Base64 Platform Runtime Core Signature Asset]",
  "laheType": "COMMIT",
  "correlationId": "corr-99821-bian-settlement-flow"
}
II. Minimum Viable Evidence Bundle (MVEB) Reference Attributes
The immutable verification components packaged for the Recomputation-as-a-Service (RaaS) engine to support zero-knowledge auditing:
Globally unique tracking identifier mapped using the ordered UUIDv7 standard.
The active 256-bit platform Policy Hash used to verify the transaction thread during triadic adjudication.
The canonicalised input data block, maintaining cryptographic hashes of application payloads with sensitive PII stripped.
An indexed array mapping the traversal path of the Agreement DAG, matching execution nodes directly to high-precision hardware timestamps.
Physical hardware memory addresses pointing to platform TPM v2.0 measurements and enclave cryptographic signatures.
A deterministic pseudorandom number generator (PRNG) seed used to verify probabilistic risk and scoring calculations.
The digital signature generated by the platform core key of the DRAGON Engine, certifying the absolute legitimacy of the proof capsule.
TRS-MS Capability Sets
The named capability products hosted within the Trust, Risk & Security Management layer of the onePOI.online Architecture.
Bedrock TRS
Cryptographic root-of-trust and high-assurance key management foundation for Trust, Risk & Security.
Inspector
Automated compliance auditing, SBOM configuration scanning, and secure regulatory observation interfaces.
Posture 360º
Platform-wide Integrated Posture Management, embedding deterministic Deontic logic constraints directly into physical computing hardware.
KeyMESH
Sovereign Cryptographic Router separating tenant secrets and private keys inside hardware-isolated enclaves.
oneCERT
Continuous hardware attestation and HBOM validation engine securing edge terminals and computing nodes.
Silicon Root-of-Trust for Fiduciary Execution & Value Settlement
Every commercial transaction, banking credential, or autonomous financial settlement fundamentally requires an uncompromised physical trust root. The Salient FinTech Innovation Set provides the non-negotiable trust engine for the TRS-MS bedrock. By executing payment tokenization, biometric verification, and ISO 20022 message signing inside hardware-isolated enclaves, it guarantees that tenant secrets and financial transaction flows remain immune to host operating system compromises, hypervisor escapes, or side-channel snooping.
Hardware Enclave Isolation (oneVault MESH)
Multi-tenant cryptographic keys and private payment credentials run strictly within TEE hardware enclaves with memory encryption keys rotated per transaction stanza.
Wire-Speed SmartNIC DPU Clearing
Network packets carrying financial payloads undergo cryptographic signature verification and eBPF membrane filtering directly on SmartNIC DPUs at wire speed before touching application memory.
Continuous Attestation (oneCERT)
Hardware Bill of Materials (HBOM) and firmware states are verified against cryptographic reference manifests, guaranteeing that all banking nodes maintain continuous Authority to Operate.
Commission a 5-Day Architectural Discovery Sprint
Accelerate your path to sovereign digital commerce. In five intensive working days, our principal systems architects map your enterprise operational perimeters directly against the Six-Fold Symphony of Systems architecture.
Complete audit of current touchpoints against SoE, SoA, SoO, SoR, SoI, and TRS-MS boundaries.
Translating legacy silo APIs into canonical semantic service domains and Agreement DAG schemas.
Token Gantry and TEE isolation sizing for zero-leakage payment and identity workflows.
Boardroom-ready blueprint with targeted milestones for the Q4 2026 / 2027 production target state.
*Fixed-price introductory engagement for qualified enterprise tenant cohorts. Deployed exclusively to your designated sovereign boundary.
The Complete SABSA Matrix & TrustOps, RiskOps, SecOps Triad
The Trust, Risk & Security Management System (TRS-MS) implements the full Sherwood Applied Business Security Architecture (SABSA) 6x6 matrix, establishing two-way traceability from boardroom risk appetite down to silicon execution barriers. Operational governance is continuously enforced through the symbiotic triad of TrustOps, RiskOps, and SecOps.
TrustOps (Assurance Management)
Establishes cryptographic truth across hardware, software, and identity. Governs OpenTitan silicon roots-of-trust, locked 9-category CycloneDX xBOM manifests, decentralised PKI lifecycles, and bitemporal Merkle state proofs.
RiskOps (Algorithmic Adjudication)
Evaluates real-time parameterised risk envelopes, counterparty velocity limits, and causal telemetry. Directly links operational security posture to Basel IV capital adequacy and automated dynamic insurability.
SecOps (In-Kernel CSMA Fabric)
Executes distributed wire-speed defence across the Cybersecurity Mesh Architecture (CSMA). Enforces SmartNIC eBPF/XDP packet filtering, zero-trust microsegmentation, and sub-nanosecond physical tamper zeroisation.
Continuous Constitutional Authority to Operate (CC-Ato)
Traditional compliance treats authorisation as a static, periodic check conducted annually. The TRS-MS architecture formalises Continuous Constitutional Authority to Operate (CC-Ato) as an unbroken mathematical conjunction across seven operational pillars:
Authorisation transitions across eight formal lifecycle states: Eligible → Attested → Certified → Active → Continuously Re-substantiated → Degraded → Suspended → Remediated. Workloads maintain an active lease through continuous sub-second cryptographic heartbeats emitted across the CSMA mesh. Non-critical warnings shift the Policy Hash to Degraded, isolating sensitive endpoints while preserving baseline operations; critical breaches trigger an instant sub-20ns line-cut, isolating the component and initiating automated Contrary-to-Duty (CTD) compensating sagas.
Six-Layer SABSA Traceability Architecture
Codifies multi-tenant commercial covenants, sovereign jurisdictional boundaries, and statutory mandates (DORA, MiCA, NIS2, GDPR, EAA).
Establishes the separation between intelligence and authority ($I \not\vdash A$), Hohfeldian deontic normative graphs, and zero-trust domain models.
Defines BIAN v14.0 service domain schemas, Agreement DAG state machines, zero-knowledge proof circuits, and capability access tokens.
Implements silicon invariants, the DRAGON triadic coprocessor, Sentient Membrane active tamper meshes, and Q32.32 fixed-point arithmetic.
Integrates seL4 microkernel separation, SmartNIC eBPF/XDP verifier maps, Wasm sandboxes, and CEN/XFS4IoT encrypted peripheral buses.
Governs continuous runtime attestation, automated key rotation, autonomous breach quarantine, and real-time supervisory telemetry.
The 18 Constitutional Jurisprudence & Hardware Reality Pillars
Uniting 10 Silicon Execution & Spatial Intelligence Pillars with 8 Socio-Legal Jurisprudential Safeguards
Part I: 10 Silicon Execution & Spatial Intelligence Pillars
1. Sheaf Gluing across 5-Tier Axiom MESH: Local truth evaluations glue into global Grothendieck sheaves; SMT provers detect boundaries.
2. Sub-20ns Line-Cut VETO & Sub-2.3 KB MVEB: Hardware interdiction drops frames in < 20ns and seals context for TopHAT review.
3. CTD Polyadic LAHE Hyperedges: Resolves primary, secondary, and reparative obligations via nilpotent semirings.
4. Algebraic Semiotics & Hohfeldian Topoi: Category-theoretic preservation of legal conceptions across compilation.
5. 10,240-bit Bipolar SB-HVSS Hypervectors: Vector Symbolic Architecture for constant-time associative matching.
6. Dual-Tier Memory Decomposition: Pool A runtime SRAM vs Pool B immutable Merkle HyperDAG; 2D Laplace calculus.
7. Spectral Radius Bounding (\(\rho(T) < 1.0\)): Tikhonov damping matrices suppress risk feedback oscillations.
8. Non-Euclidean GraphHopper .ghz Floor: Real-world micro-isochrones anchor neuro-symbolic JEPA world models.
9. Multi-Modal Contextual Energy Barrier: \(E_{\text{total}} \to \infty\) renders unlawful actions mathematically uncomputable.
10. Lean 4 / Z3 SMT Formal Proof Loops: Interactive and automated proofs of Non-Contradiction before silicon deployment.
Part II: 8 Socio-Legal Jurisprudential Safeguards
11. Cartographic Void Abstention (Leone/Wagner): Protects informal routes from cartographic erasure via Shadow-Way hyperedges.
12. Derridean Singular Gift (de Ville/Derrida): Ephemeral Nonce = 1 OBO Warrants allow human judicial mercy without rule ossification.
13. MVEB Holographic Decompression (Wolcher): Unfolds 2.3 KB bundles into experiential human narratives, sensor traces, and collision graphs.
14. Hegelian Immanent Critique (Salter): oneWallet citizen harm petitions challenge internally consistent but substantive unjust rules.
15. Hart Open Texture & Penumbra Interdiction (Jackson/Santos): Halts autonomous extrapolation at penumbral boundaries; generates BRB dossiers.
16. Husserlian Prose-to-Glyph Canvas (Broekman): Isomorphic round-tripping between natural human legal prose and formal bytecode.
17. Deleuzian Sunsetting & Volume Floors (Lippens): Mandatory bitemporal expiry epochs prune obsolete regulations and prevent over-coding.
18. Diachronic Drift Disentanglement (Balkin/Paul): Dual-mode Policy Hash auditing tracks ideological drift without breaking historical seals.
The Two-World-Model Architecture (POFT-PP-DIKWT Across 9 xBOMs), 36-Cell SABSA Crosswalk & 17-Framework FSI Threat Matrix
onePOI.online does not attempt to make a probabilistic neural model infallible; it places probabilistic neural world models (JEPA / LNN / WSP) inside a hardware-anchored Phygital Symbolic World Model (CFKG & B-HGNN). This unified World System operationalises all 11 Organisational & Epistemic Dimensions (People, Organisations, Functions, Tactics, Processes, Procedures, Data, Information, Knowledge, Wisdom, & Technology – POFT-PP-DIKWT) across the locked 9-Category CycloneDX 2.0 xBOM and all 36 Cells of the 6 × 6 SABSA Matrix.
| SABSA Layer | Assets (What) | Motivation (Why) | Process (How) | People (Who) | Location (Where) | Time (When) |
|---|---|---|---|---|---|---|
| 1. Contextual | 12 NEO-ERP Sector Cohort Value Chains & 40/40/20 FinOps | Regulatory Insurability Moat & BoE/FCA 80%-vs-2% Bridge | Cross-Sector Cohort Charter Workflows | Cohort Boards, SM&CR Senior Managers & Citizens | Federated Sovereign Nodes (UK/IE/DE NODE) & 18 Spokes | Q4 2026 Discovery → 28 June 2030 EAA → 2033 Singularity |
| 2. Conceptual | Two-World-Model Coupling & POFT-PP-DIKWT Ontology | Intelligence ≠ Authority (\(I \neq A\)) & DORA Art. 28 Survivability | 5 Graph Overlays of Meta-CFG (\(\mathcal{G}_N, \mathcal{G}_O, \mathcal{G}_A, \mathcal{G}_P, \mathcal{G}_C\)) | Triadic Separation: TopHAT, DRAGON, Conductor | SB-HVSS & Cartographic Void Abstention Zones | Dual-Axis Bitemporality (\(T_v \times T_t\)) & Silicon Eternity Clause |
| 3. Logical | Master Policy Hash (\(\mathcal{PH}\)) sealing 9 CycloneDX 2.0 xBOMs | Deontic Dominance (\(\mathbf{F} \succ \mathbf{O} \succ \mathbf{P}\)) & Lawvere Adjoint Proofs | Categorical Pushouts (\(Q_1 \coprod_{Q_0} Q_2\)) & Path Obliteration (\(\mathbf{G} - \mathbf{\Delta E}\)) | Polyadic LAHE Hyperedges & UEBA 2.0 Trust Decay | Non-Euclidean GraphHopper Micro-Isochrone Floor & BIM | LACE 2D Laplace Transform \(F(s_1, s_2)\) & Pole-Zero Stability |
| 4. Physical | Incidence Matrices \(\mathbf{H}(T_v, T_t)\), B-HGNN & MVEB Capsules | Sub-Software Zero-TOCTOU Enforcement & PQC Immunity | 3-Pass Pipeline: DPU (\(\le 8.2\,\mu\text{s}\)) → SRAM (\(\le 15\,\mu\text{s}\)) → TEE (\(\le 45\,\mu\text{s}\)) | Hardware SPIFFE/SVIDs, oneWallet Pods & TPM 2.0 Roots | Dual-Tier Memory (Pool A SRAM / Pool B CXL) & POI Appliance | Sub-15μs Adjudication, <45μs ZKP & WSP ODE Integration |
| 5. Component | Stanzas as SBOMs with Intrinsic CFGs, Glyphs & VEX | Leontief Inheritance \((\mathbf{I}-\mathbf{D})^{-1}\vec{v}_0\) & Safe-Tube Proof | Agentic SAST/DAST/IAST/RASP/APM & Synthetic Data Factory | oneCDE.online & TopHAT Workbenches, Zenjin & oneCERT | Container OBOMs, CEN/XFS4IoT Buses & 0x5501 CEP Headers | Build-Time AST Pushout → PTP Nanosecond Glyphs → Key Rotation |
| 6. Operational | Live Posture 360 Vector, inSight 360 & Notary HyperDAG | Continuous Authority to Operate (cATO) & 17-Framework Defence | "Just-Ahead" TEE Simulation & "Just-in-Time" Tier 3b Emulation | TrustOps, RiskOps, SecOps (TRS-MS) & FSI Fusion Centres | 18 Operational Spokes & Offline Constitutional Island Mode | Continuous 24/7 Heartbeat, CTD Sagas & Bitemporal Replay |
Enterprise v20, Mobile & ICS
Covers 15 Enterprise tactics (Stealth & Defense Impairment), iOS/Android mobile banking apps, and ICS/OT vault, HVAC, and CEN/XFS4IoT hardware.
F3, ATLAS, EMB3D, FiGHT & DISARM
Unifies MITRE F3 (APP fraud & mule networks), ATLAS (LLM/AI poisoning), EMB3D (HSM/POI firmware), FiGHT (5G signalling), and DISARM (deepfakes/bank-run disinfo).
FS-ISAC, OWASP & CAPEC
Bridges SOC and AML via the 5-phase FS-ISAC Cyber Fraud Framework, OWASP Top 10 / API / Agentic ASI01–10 / MCP, and MITRE CAPEC exploit patterns.
D3FEND, Engage, Diamond & CRI
"D3FEND is the map; CFKG is the fence." Combines D3FEND, MITRE Engage decoys, Unified Kill Chain, Diamond Model, CWE/CVE/EPSS, and >2,100 CRI Cyber Profile controls.
Operationalising EN 18286:2026 (Decision (EU) 2026/2274) – The 4-Tier Integrated Management System (IMS) & Bronze / Silver / Gold Assurance Profiles
Published in the Official Journal of the European Union (OJEU) on 14 October 2026 via Commission Implementing Decision (EU) 2026/2274 and developed by CEN/CENELEC JTC 21, EN 18286:2026 is the first European harmonised standard operationalising Article 17 (Quality Management System – QMS) and Article 11 (Technical Documentation) of the EU AI Act. Complying with EN 18286:2026 grants high-risk AI providers a statutory Article 40 Presumption of Conformity ahead of the Digital Omnibus enforcement deadlines (2 December 2027 for Annex III standalone high-risk AI; 2 August 2028 for Annex I embedded safety components). Whereas corporate ISO/IEC 42001 (AIMS) certification permits risk-appetite exclusions via a Statement of Applicability (SoA), EN 18286:2026 operates under non-derogable product safety law protecting health, safety, and fundamental rights (Article 9) with zero control opt-outs across all 13 obligations of Article 17(1)(a)–(m).
| Governance Dimension | Tier 1: ISO/IEC 27001 & 27002:2022 (ISMS) | Tier 2: ISO/IEC 42001 (AIMS) | Tier 3: EN 18286:2026 (Harmonised AI QMS) | Tier 4: onePOI.online L6 TRS-MS Bedrock |
|---|---|---|---|---|
| Scope & Structural Target | 93 streamlined controls across Organisational (37), People (8), Physical (14), and Technological (34) themes + Attribute Views |
Organisation-wide AI governance, AI literacy, acceptable use, and third-party oversight across Clauses 4–10 | Product-specific high-risk AI lifecycle across Clauses 4–10, 5 Lifecycle Stages, and Normative Annexes A, B, C, ZA |
Hardware instructions, SmartNIC packets, 2nm SRAM Compute-in-Memory (CIM) bitlines, and bitemporal CFKG hyperedges |
Control Opt-Outs (SoA) |
Permitted via management Statement of Applicability (SoA) |
Permitted via management Statement of Applicability (SoA) |
Zero Opt-Outs: Statutory product law mandates all 13 Article 17(1) obligations | Non-Derogable Dominance ($\mathbf{F} \succ \mathbf{O} \succ \mathbf{P}$): Prohibitions physically uncomputable |
| Primary Risk Lens | Internal Confidentiality, Integrity, & Availability (CIA) + EU AI Act Art. 15 Cyber Baseline |
Balancing internal enterprise objectives, commercial risk appetite, and AI ethics | External protection of human health, safety, and fundamental rights (Article 9) | Elimination of Supervision Debt via < 20 ns XDP_DROP & < 45 μs DRAGON VETOs |
| EU Art. 40 Conformity | No | No (delivers 60%–70% organisational governance foundation only) |
Yes (Decision (EU) 2026/2274) for Art. 17(1) & Art. 11(1) | Automated via oneCERT Dual-Layer Annex IV Dossiers + < 2.3 KB Groth16 MVEBs |
Bronze Assurance Profile (< 20 μs)
Deploys on commodity x86 and ARM cloud virtual machines using Linux Kernel eBPF / XDP inline membranes paired with the software Formal Verification Engine (FVE). Compiles identical PIME Deontic Agreement DAGs over the Control-Flow Knowledge Graph (CFKG) and emits valid 4D xBOM Passports and Minimum Viable Evidence Bundles (MVEBs) for immediate EN 18286:2026 and ISO/IEC 42001 conformity.
Silver Assurance Profile (120–180 μs)
Executes inside hardware-attested Confidential VMs (AMD SEV-SNP, Intel TDX, ARM CCA) accelerated by commercial SmartNIC DPUs and cloud FPGA Block RAM (BRAM) High-Level Synthesis (HLS) bitmasks. Adds remote hardware attestation via Kali Remote Attestation Services (Kali RAS) ahead of the 2 December 2027 Annex III gate.
Gold Assurance Profile (< 20 ns / < 45 μs)
Combines AMD Pensando / NVIDIA BlueField SmartNIC DPUs (< 20 ns XDP_DROP) with custom 2nm SRAM CIM DRAGON and LACE ASICs (< 45 μs triadic VETO at > 1,000,000 msg/s). Substantiates a 15%–30% reduction in Operational Risk Capital Reserves under the Basel III/IV Standardised Measurement Approach (SMA) and EU DORA Article 6 via clean-room RaaS supervisory sandboxes.
You've Explored the Full Symphony
From the Constitutional Bridge of the SoE to the Financial-Grade Bedrock of TRS-MS – the Symphony of Systems is a single, coherent Constitutional Operating System. Every layer governs. Every act is lawful. Every audit is deterministic.