Where Switcher+
Fits
Switcher+ is a productised capability set and specialised multi-tenant POI (Point of Interaction) appliance form factor within the onePOI.online ecosystem – the platform's agentic concierge for onboarding, switching, and physical fulfilment. It transforms high-friction lifecycle events – such as service migration, identity recovery, and multi-sector onboarding – into deterministic, hardware-anchored, phygital (physical + digital) experiences.
Operating at the intersection of the System of Orchestration (SoO) and the System of Engagement (SoE), Switcher+ packages the governed runtime of the platform's Conductor, turning complex, multi-party workflows into single-session, cryptographically-sealed interactions – whether at a bank branch, a retail counter, a drive-through kiosk, or a community hub.
Runs on the Constitutional Operating System (COS) with FIPS 140-3 Level 3 HSM anchoring, DRAGON Engine adjudication (<100 µs), and full oneWallet.online EUDI credential interoperability. The constitutional chain is invariant: iEngine (SoI) proposes, DRAGON adjudicates, Conductor (SoO) executes, Switcher+ fulfils – acting as the physical actuator at the edge.
Core Strategic Principles
Compliance-by-Construction
Deterministic GovernanceRenders unauthorised actions structurally impossible at runtime and makes all execution forensically attributable. Eliminates reactive "Log Archaeology" and satisfies DORA, PSD3, and AMLR.
Pooling Economy of Scale
Infrastructure SharingCapital costs for sensory hardware are pooled across a multi-tenant cohort (banks, telcos, government), allowing smaller enterprises to leverage forensic-grade tools.
Phygital Symbiosis
Digital Twin AnchoringCredentials (SIM, card, ID) are linked to a Digital Twin in oneWallet.online, enabling biometric-driven "Resurrection Workflows" for lost assets.
Authority-Poor Executive
Separation of PowersThe SoO Conductor has zero standing privileges; it cannot move data or value without a cryptographically signed Lawful Warrant, preventing agentic sprawl.
Zero-Trust Phygital Edge
Forensic Sensory ArraysTamper-evident edge appliances featuring stereoscopic UV/IR/white-light imaging, 3D NIR face contours, and ISO 30107-3 L2 biometric PAD.
U³ Inclusion Engine
Universal AccessEnsures universal access across smartphone and non-smartphone interfaces with Conversational UI (CUI) plain-language contract translation.
Component Architecture
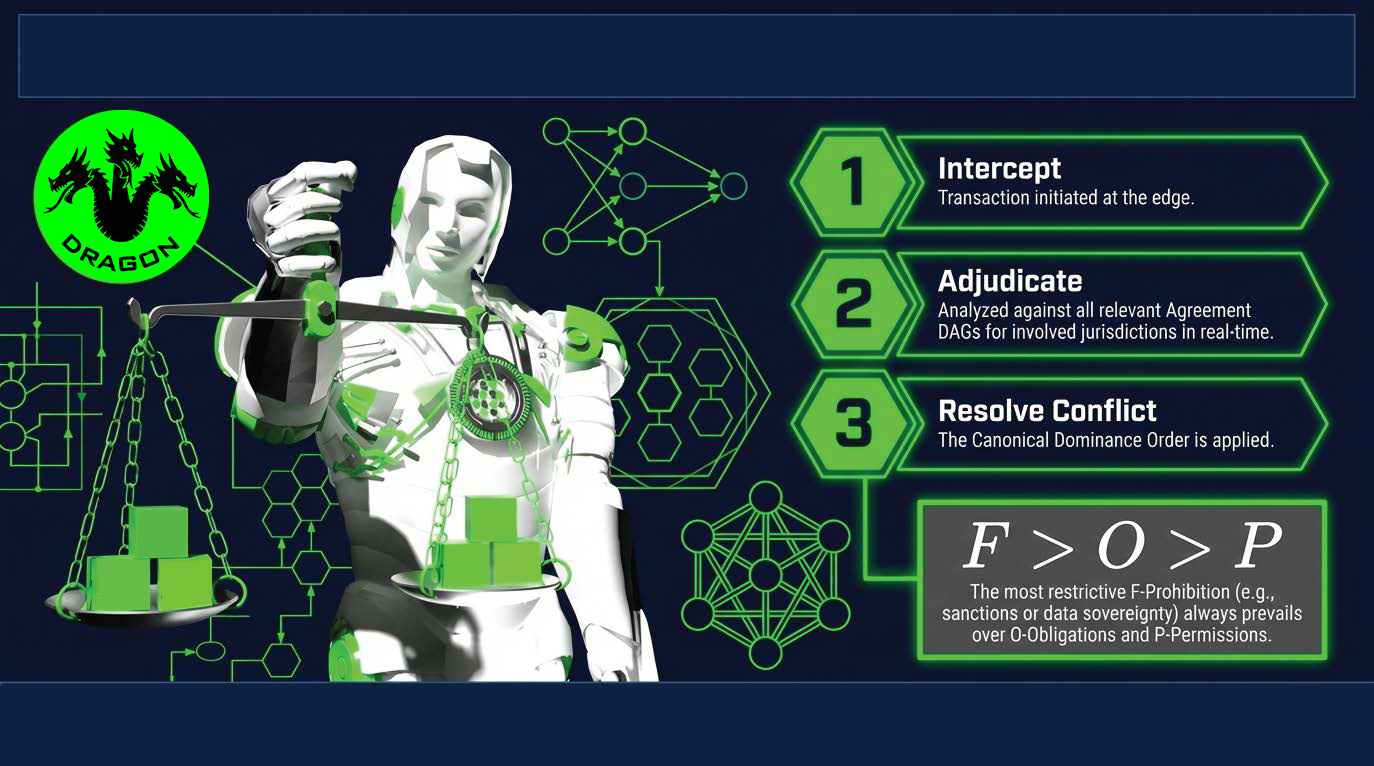
Deterministic Adjudication at the Edge: A consequential event begins as a proposed intent. The System of Intelligence (iEngine) enriches that intent with context, but DRAGON adjudicates according to the active Agreement DAG. The canonical rule F > O > P guarantees that a Prohibition strictly dominates an Obligation, which strictly dominates a Permission. Switcher+ never acts as an engine or brain – iEngine proposes, DRAGON adjudicates, Conductor executes, Switcher+ fulfils.
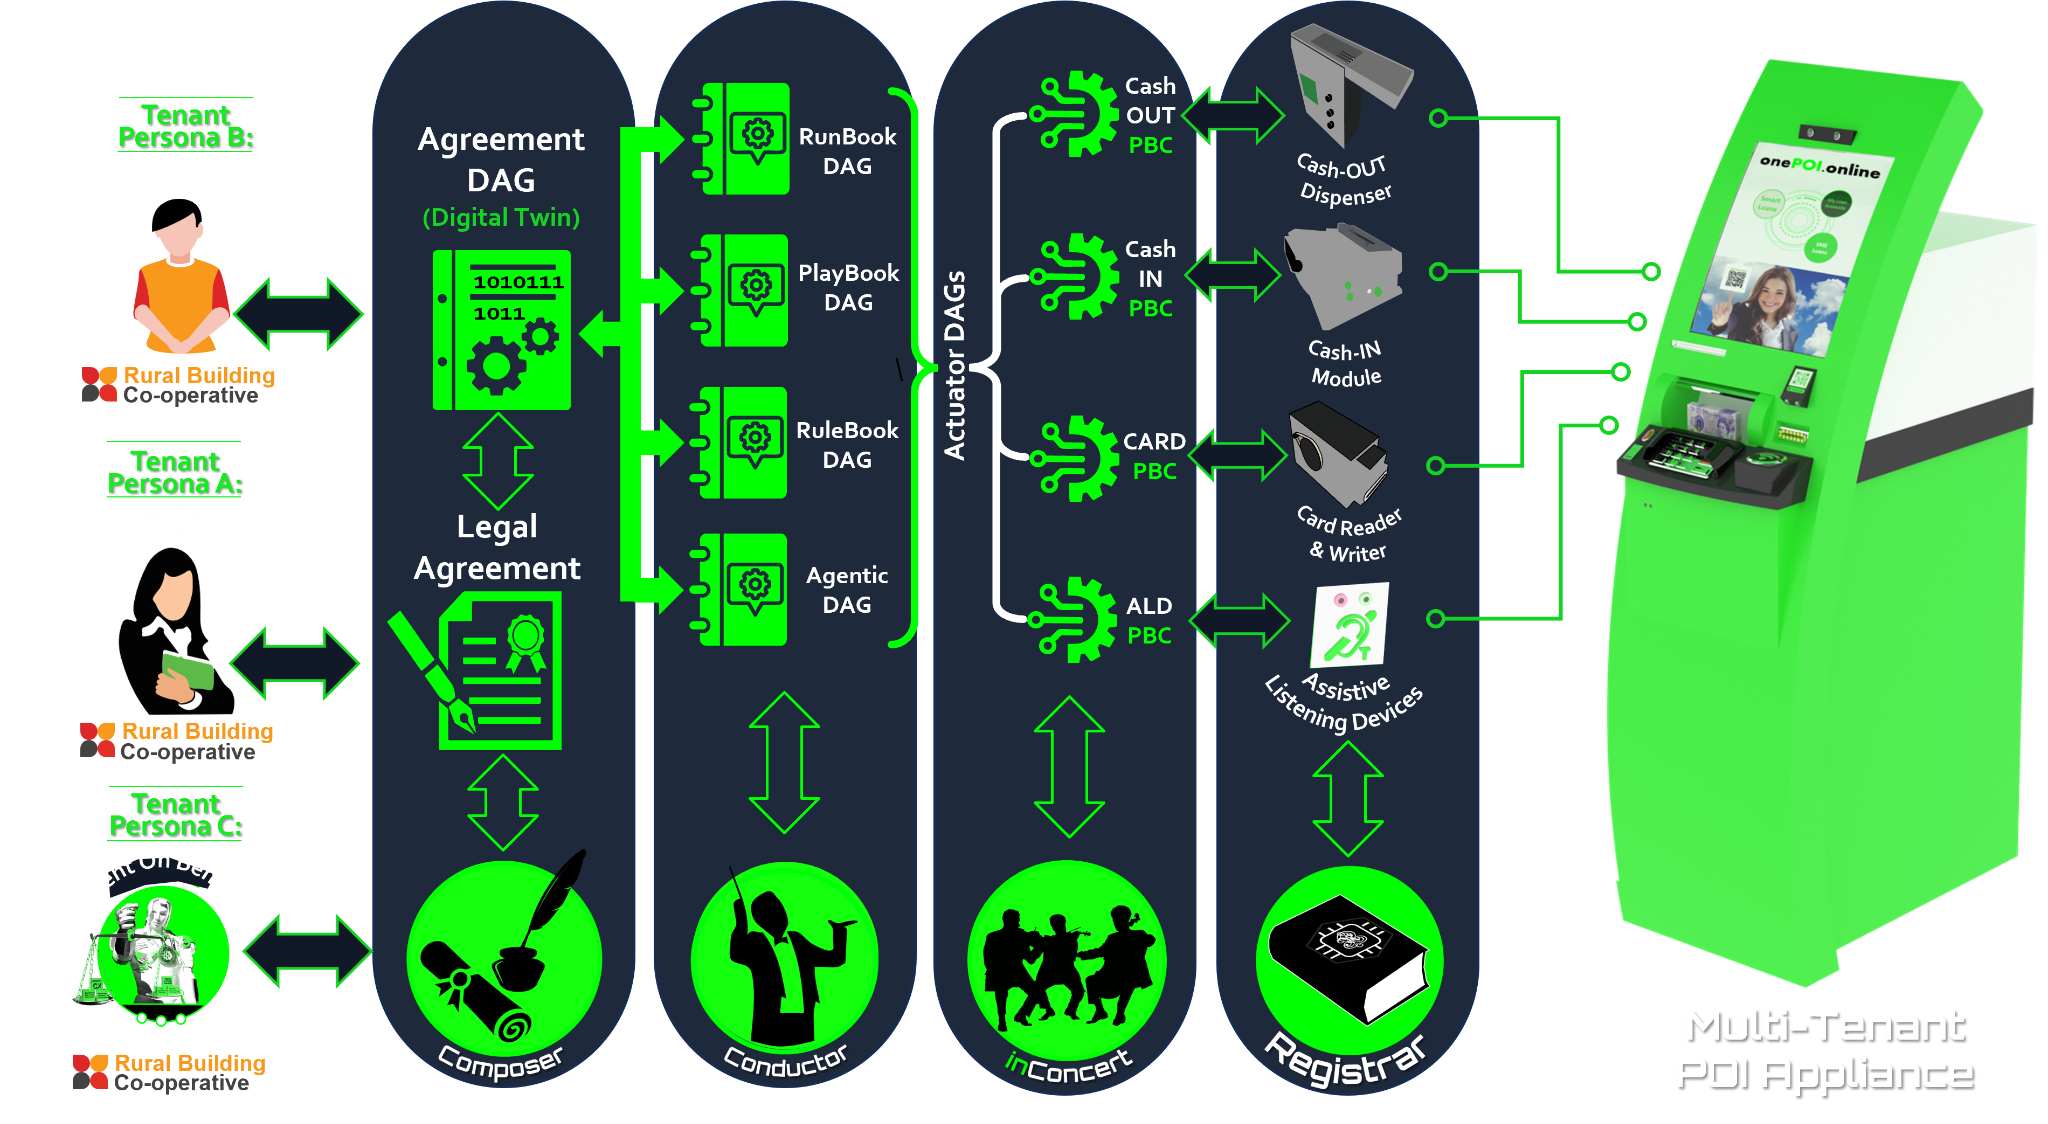
Agreement-DAG Driven Multi-Tenancy: Tenant personas bind to legal agreements represented as Agreement DAGs. Runbook, Playbook, Rulebook, and Agentic DAGs drive Actuator DAGs, which in turn invoke Packaged Business Capabilities (PBCs) on financial-grade peripherals. Peripheral actions – cash dispense, card issuance, biometric scan – are the deterministic end of a policy chain, ensuring zero cross-tenant execution bleed.
Five integrated subsystems form the Switcher+ appliance – from the platform's Conductor (SoO) to the edge compute layer – each component hardware-attested and constitutionally governed.
Operating in absolute harmony with oneWallet.online, Switcher+ serves as the physical edge execution arm for sovereign digital identity. Through the Customer Attribute Management System (CAMS), Switcher+ dynamically maps physical interactions directly to the user's sovereign credential enclaves, establishing a hardware-attested, multi-tenant bridge where user attributes are processed on-demand with zero data leakage.
Conductor Execution (SoO)
The Conductor RuntimeThe platform's Conductor runtime executes Switcher+ Capability Profiles as Actuator DAGs inside a secure, hardware-isolated WebMCP WASM Sandbox. It implements the Neuro-Symbolic Sandwich, wrapping the AI-driven Conversational UI (CUI) in a deterministic deontic logic compiler. This restricts the agent's Action Space; if an AI agent generates an execution path outside the active Agreement DAG, the sandbox triggers an automatic Structural VETO, preventing malicious state transitions.
Document Imaging Core
Stereoscopic VerificationDual UHD stereoscopic lens array evaluating security marks across UV, IR, white-light, and coaxial wavelengths. Certified to ICAO 9303 / ISO/IEC 19794 standards for travel and identity documents.
Biometric Authentication
3D NIR Liveness3D NIR structured-light projection with rPPG liveness detection and presentation attack detection (PAD) to ISO 30107-3 Level 2. Biometric templates never leave the secure enclave.
Hardware Security Module
FIPS 140-3 Level 3FIPS 140-3 Level 3 HSM with CC EAL5+ tamper-evident enclosure. All biometric templates processed within TEE – never exported. Cryptographic key ceremony and lifecycle fully automated via Constitutional warrants.
Edge Compute & Network
Autonomous Edge ResilienceARM-based SoC with dedicated NPU for on-device ML inference. Supports Autonomous Edge Resilience for offline autonomy. Pre-cached safety-critical axioms govern edge actions, which are committed locally and reconciled via Bitemporal Ledger recomputation upon network reconnection, guaranteeing historic ledger mathematical validity.
Product Capabilities
Six governed product capabilities delivered through a single phygital session – each sealed with Lawful Act Hyperedge receipts and orchestrated by the Conductor runtime.
Zero-Device Recovery
Survive device loss seamlessly. Proving identity via the Multi-Modal Biometric Gauntlet (stereoscopic document scan, 3D NIR face map, and rPPG liveness) triggers an O(1) constant-time lookup to locate the sovereign oneWallet.online anchor, instantly re-binding attributes without high-friction re-onboarding.
iEngine Offer Recommendations
Queries the user's consented profile from the oneWallet.online Consent Engine using Open Banking AISP frameworks. The iEngine (SoI) generates real-time facility options (e.g. customised loan/credit terms) – surfaced by Switcher+ and translated into plain natural language by the Conversational UI (CUI).
Phygital Onboarding
Start service migration or credential provisioning on the phone via oneWallet.online, and complete high-assurance biometric verification at any physical Switcher+ edge appliance. Connects digital convenience with forensic physical security.
Multi-Sector Onboarding
Simultaneous enrollment across banking, healthcare, and utilities in one session. Facilitates Governance-as-a-Service (GaaS): tenants pay micro-royalties for utilising verified cryptographic liveness and identity proofs minted by peers during the session, converting compliance overhead into a recurring revenue stream.
Kinetic Fulfilment & Cash-In
Convert physical cash into digital value or physically print secure tokens. Ephemeral cryptographic keys are generated in local TEE enclaves and split across the mesh using Threshold Cryptography (MPC), preventing edge extraction of private key material.
LockerShop & 3PL Fulfilment
Physical handoffs and secure logistics. Links Switcher+ edge cabinets to the platform's System of Orchestration, which executes autonomous cargo delivery and pickup governed by cryptographically signed warrants and user consent DAGs.
Regulatory & Standards Alignment
Switcher+ is architected to operate within the most demanding regulatory environments – with compliance enforced at the silicon boundary, not bolted on as an afterthought.
Regulatory Frameworks
Technical Standards
Beyond the Digital-Only
Paradigm
Unlike purely-digital onboarding platforms, Switcher+ operates at the phygital boundary – the moment where identity is proven, payment moves, data is exchanged, and governance applies. Traditional digital-only platforms rely on software-level trust (API keys, OAuth tokens).
Switcher+ anchors trust in hardware-attested silicon enclaves, making non-compliance structurally impossible rather than merely detectable. This is not a policy engine bolted onto an API gateway – it is a Constitutional Operating System where the silicon itself enforces the law.
Syntactic, semantic, and pragmatic compliance checks at silicon speed.
CC EAL5+ tamper-evident enclosure with TEE-isolated biometric processing.
3D NIR structured-light with rPPG liveness – defeating deepfakes and replay attacks.
Full governance enforcement without network connectivity – deterministic sync on reconnect.
Architectural Evaluation & Risk Analysis
A transparent decomposition of the system's core capabilities, operational trade-offs, and risk mitigations for enterprise committees and risk boards.
Core Architectural Strengths
-
Substantiated Integrity (Basel IV Capital Relief): Relocating compliance directly to physical enclaves ensures that all transactions are mathematically compliant at runtime. High-fidelity bitemporal transaction logs and hardware-enforced deontic guardrails lower operational risk indices, allowing FSIs to release capital reserves under Basel IV.
-
Full Interoperability (eIDAS 2.0 & ARF): Cryptographically snap-to-grid with the EUDI Wallet Architecture Reference Framework (ARF). Operates out-of-the-box with European Qualified Electronic Attestation of Attributes (QEAA) standards.
-
O(1) Identity Restoration: Lost devices or credentials can be biometrically resurrected at the physical boundary in constant time. Leverages the Multi-Modal Biometric Gauntlet to re-anchor the person directly to their existing oneWallet.online DToP.
Architectural Trade-offs & Risks
-
Hardware & TEE Dependencies: The platform's security guarantees are tightly coupled with physical hardware enclaves (eBPF kernel-level enforcement and the DRAGON Engine). Transitioning legacy, low-grade merchant terminals is a major dependency that requires hardware upgrades.
-
Deontic Logical Paradoxes: Competing regulatory mandates (e.g. GDPR Right to Erasure vs. AMLR Data Retention) require sophisticated deontic dominance rules (Forbidden > Obligated > Permitted) to prevent processing gridlocks inside the hardware-enforced policy adjudicator.
-
Physical Sensory Maintenance (Information Deficit): The long-term operating costs and calibration requirements of forensic-grade optical, UV, and IR sensors in high-traffic retail or civic environments remain a critical operational unknown compared to traditional ATM maintenance models.
Ready to Deploy Switcher+
in Your Estate?
Whether you are an FSI anchor seeking to extend phygital reach, a retailer transforming your counter into a governed service hub, or a public body deploying universal citizen access – Switcher+ is the agentic concierge and appliance class that makes it real.
Switcher+ Appliances operationalize high-assurance physical terminal modalities under the System of Engagement (SoE) TXM Membrane. Enabling seamless, biometric-verified session continuation from mobile to terminal without session fragmentation.